Technical University of Denmark admits breach that may have affected up to 200,000 accounts
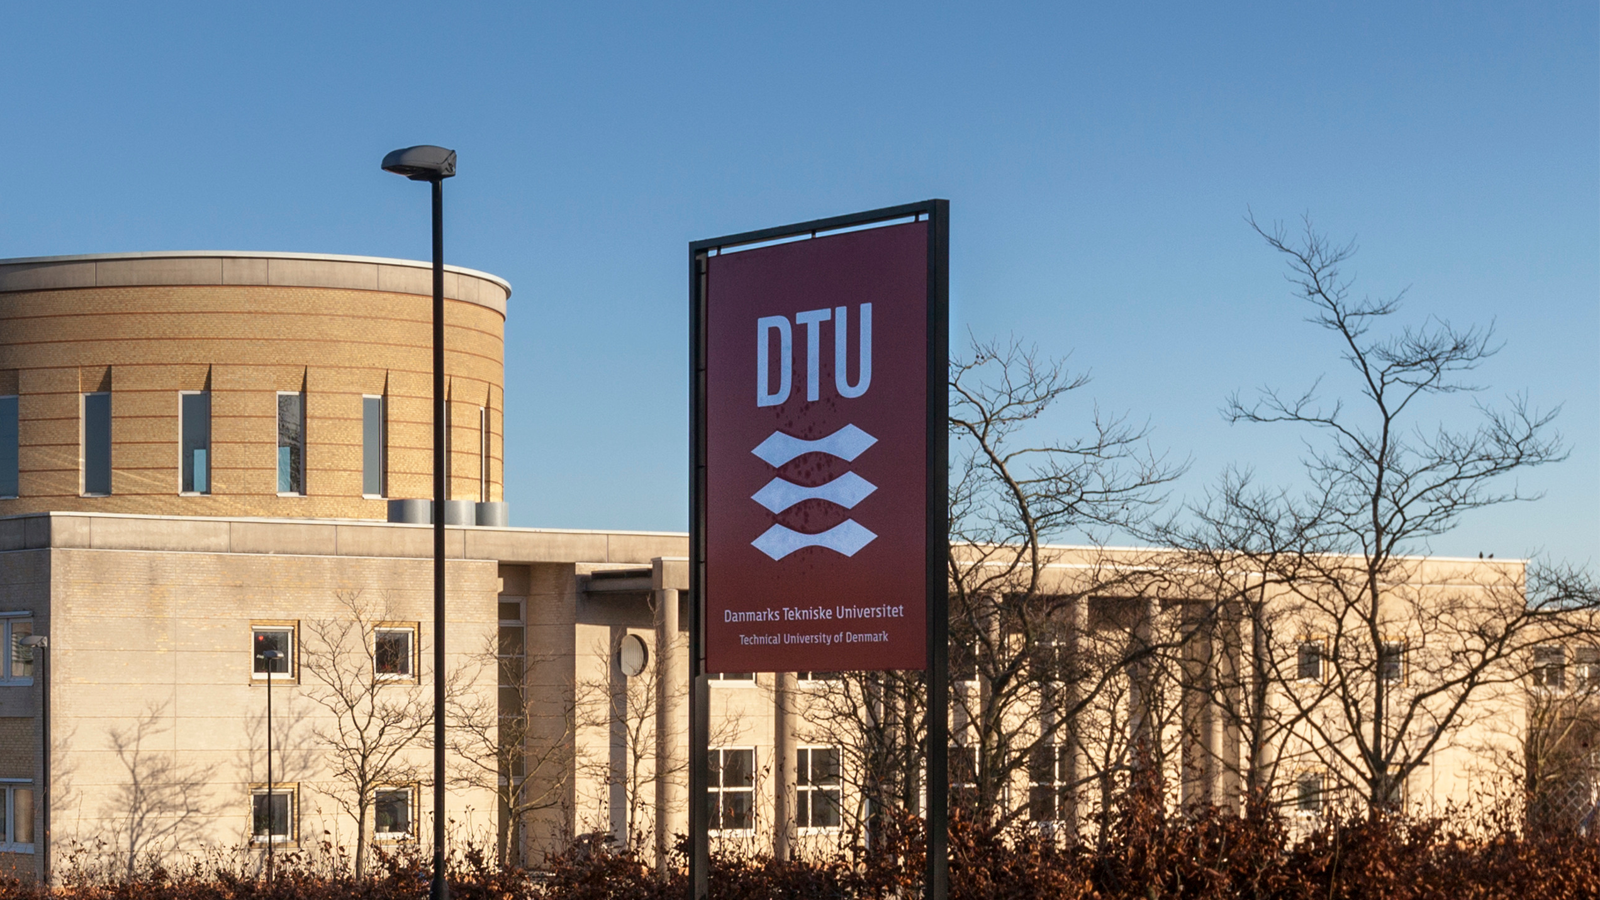
The Technical University of Denmark (DTU) disclosed that a cyber breach could have exposed personal data of up to 200,000 people after hackers breached its identity and access management system and removed a large data set.
The university said the illicit actors accessed the platform that manages user authentication and rights, copying files that hold information on students, faculty, staff and perhaps outside collaborators. DTU noted the incident was identified through routine monitoring and that an internal probe, aided by outside specialists, has been launched.
Although the complete list of compromised records remains undisclosed, officials said the stolen data may consist of names, email addresses, university ID numbers and other details usually kept in an identity store. The university has not verified if passwords or other authentication tokens were among the extracted files.
In recent years, higher‑education campuses have grown appealing to cyber‑criminals, mainly because centralized authentication services grant access to many campus services. Comparable breaches at European universities have underscored the difficulty of securing legacy IAM systems that frequently connect to both cloud and on‑premise applications.
DTU has started informing potentially impacted users and is recommending they reset passwords, activate two‑factor authentication when feasible, and stay alert for dubious messages. The institution also filed a report with Danish data‑protection regulators and is working with law‑enforcement bodies to identify the attackers.
Going forward, the university intends to carry out an extensive forensic analysis, strengthen its security framework, and evaluate adherence to the EU’s General Data Protection Regulation. Analysts warn that the incident may trigger wider examination of identity‑management protocols within academic networks, and they advise anyone whose information might have been exposed to watch their accounts for any misuse.

Comments (0)
Be the first to comment.
Join the discussion