Malicious PowerShell Phishing Campaign Hijacks Placeholder Domain ‘third‑party.com’
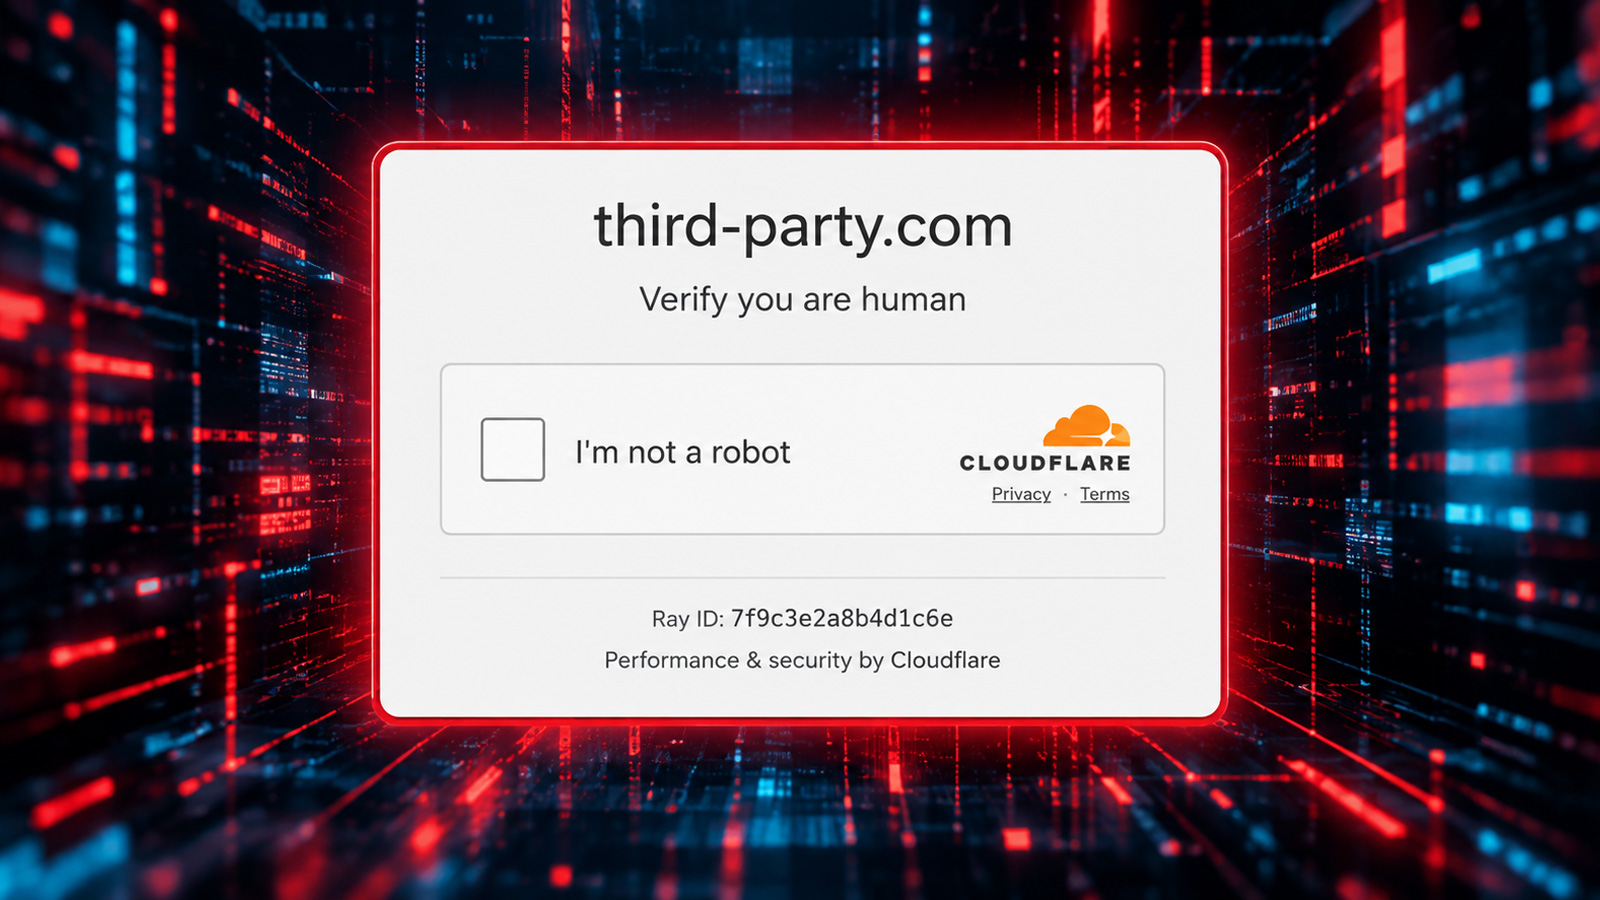
Security researchers have found that the address third‑party.com, traditionally employed as a generic placeholder in code snippets and developer documentation, is currently serving a counterfeit Cloudflare verification page intended to trick Windows users into executing malicious PowerShell commands. The finding was initially disclosed by the security news site BleepingComputer after several users reported dubious prompts.
The domain has long appeared in technical manuals as a neutral example URL, much like example.com, enabling writers to demonstrate web addresses without sending traffic to an actual site. Because the name is widely recognized as a dummy address, many developers and automated tools reference it without suspecting abuse. Since the address resolves to a live server, any material that copies the placeholder can unintentionally direct visitors to the malicious host.
In its current incarnation, the site displays a page that imitates the familiar Cloudflare challenge shown when a visitor is flagged for suspicious activity. The page asks visitors to confirm they are not a robot, but instead of a simple checkbox it provides a button that, when pressed, launches a script claiming to verify the user’s browser. The page also incorporates branding such as the Cloudflare logo and color scheme, making the ruse harder to detect for non‑technical users.
The script is designed to leverage the default behavior of Windows PowerShell, prompting users to copy and paste a single‑line command into a PowerShell window. That command retrieves and runs additional payloads from remote servers, giving attackers the ability to install malware, exfiltrate data, or maintain persistent access to the compromised machine. The retrieved payload is typically obfuscated, allowing it to evade basic antivirus scans. Once run, the code can open a reverse shell or deploy a cryptocurrency miner, depending on the operator’s goals.
Cybersecurity firms have cautioned that the attack vector depends on social engineering rather than a technical flaw, banking on users’ familiarity with Cloudflare prompts and their willingness to follow seemingly legitimate instructions. Users are urged to avoid executing code from unverified sources, to verify the authenticity of any Cloudflare challenge by checking the URL, and to keep PowerShell’s execution policy at a restrictive level. Organizations should consider disabling PowerShell remoting for standard users and employing application‑control solutions that block unsigned scripts.
The hijacking of a placeholder domain highlights a broader pattern in which threat actors co‑opt benign‑looking internet resources to boost the credibility of phishing campaigns. Defenders are advised to monitor traffic to known example domains, update security policies to flag unexpected Cloudflare verification pages, and educate developers about the risks of using real‑world domains in documentation. Researchers anticipate that similar tactics may surface on other placeholder domains, prompting a reassessment of how developers reference example URLs in public repositories.

Comments (0)
Be the first to comment.
Join the discussion