Cyberattack on Refrigeration Supplier Endangers France’s Blood Reserves
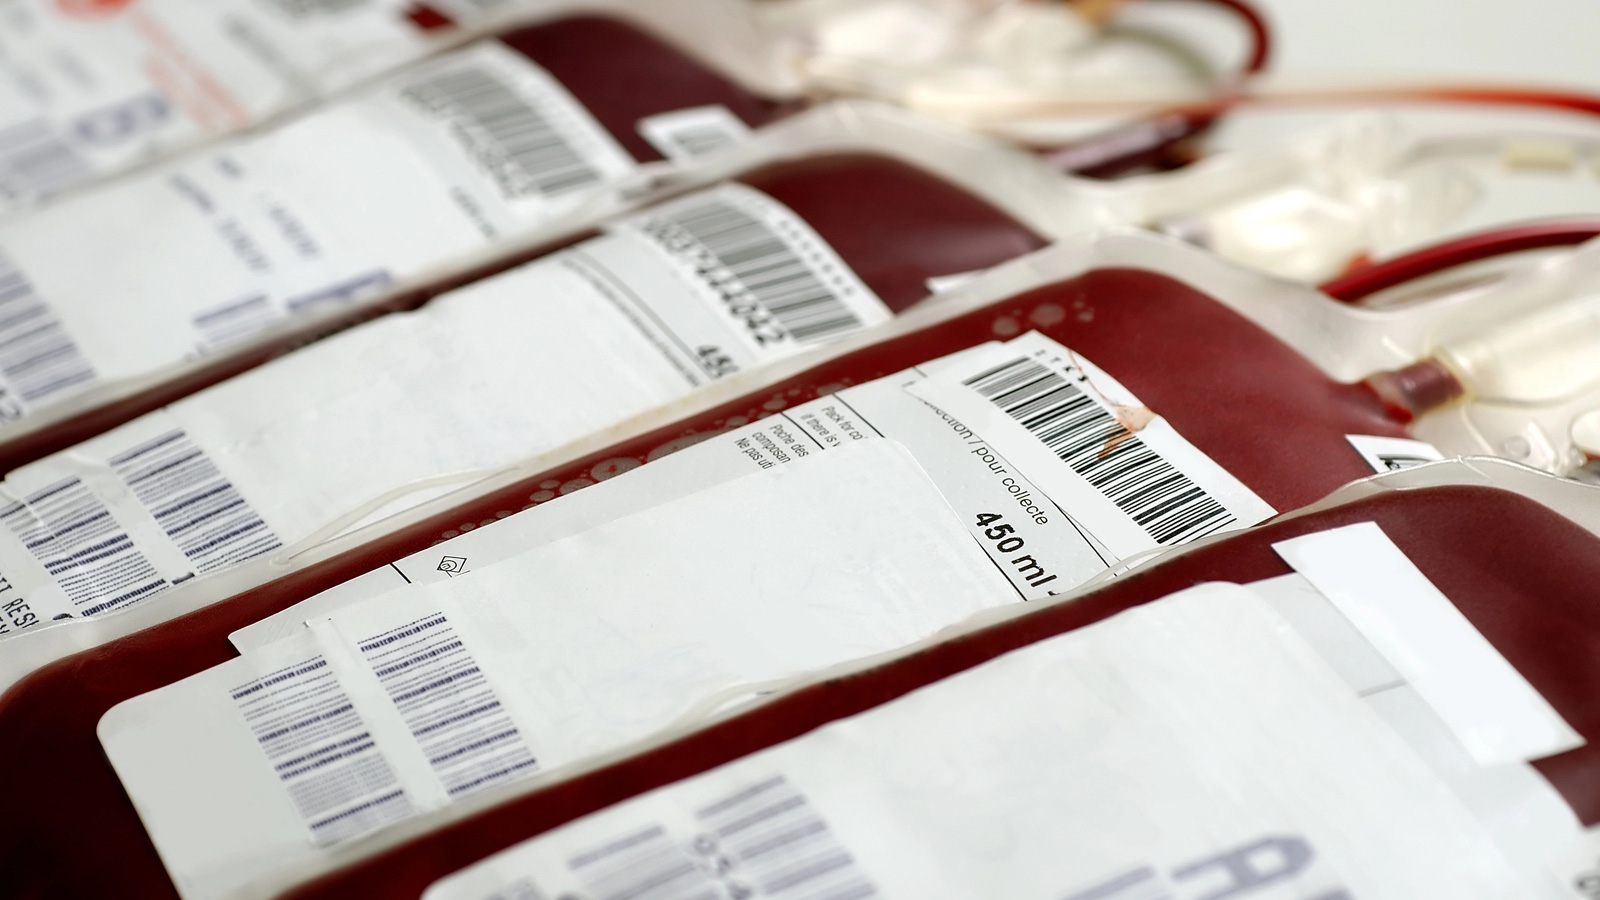
France’s national blood service announced on Tuesday that a cyber intrusion targeting a refrigeration equipment vendor altered temperature and defrost settings at three of its blood storage facilities, jeopardising millions of blood units.
The breach appears to have been aimed at the cooling‑unit provider rather than the blood service itself, prompting the agency to halt operations at the impacted sites while technicians worked to re‑establish safe temperatures. Officials warned that the incident highlights the fragility of essential health infrastructure to digital attacks.
Blood components must be stored within strict temperature ranges—generally 1 °C to 6 °C for red cells and –20 °C for plasma—to stay viable. Even short‑lived deviations can undermine the safety and effectiveness of transfusions, potentially affecting hospitals nationwide that depend on the national supply chain.
Cyber‑related assaults on medical and laboratory equipment have been on the rise as hackers exploit the growing connectivity of devices once isolated. In France, the health sector has been urged to tighten cybersecurity measures after earlier ransomware incidents disrupted hospital services. This latest case underscores the importance of supply‑chain security, particularly for vendors handling critical hardware.
In reaction, the blood service triggered its emergency contingency plan, moving inventory to alternate storage locations and intensifying temperature‑log monitoring. The agency also alerted the French cybersecurity authority ANSSI, which is now leading an inquiry into the breach and the tactics used to tamper with the refrigeration controls.
Although no immediate blood‑product shortage has been reported, the event could have downstream consequences if compromised units are deemed unusable. Health officials are asking hospitals to report any irregularities in blood quality and to adhere to revised handling protocols while the investigation continues.
Specialists suggest the incident may spark a wider reassessment of how medical facilities evaluate and oversee third‑party technology providers. Recommendations include bolstering encryption, deploying multi‑factor authentication, and conducting regular vulnerability assessments to avert similar attacks. The findings of the ongoing probe are expected to shape policy debates on protecting the nation’s critical health infrastructure from cyber threats.


Comments (0)
Be the first to comment.
Join the discussion