Russian Authorities Cripple VasyGrek Cybercrime Ring with Kaspersky Assistance
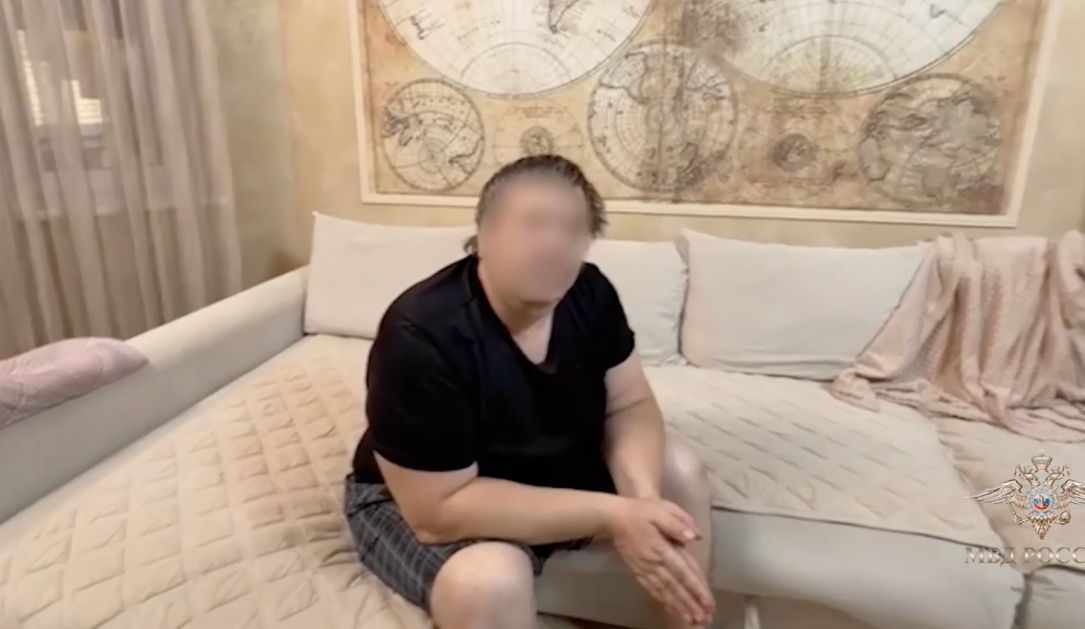
On Monday, the Russian Interior Ministry reported that law‑enforcement agents have dismantled the VasyGrek cybercrime syndicate's operational infrastructure and have pinpointed a number of its purported members. The disclosure followed a joint probe that received technical support from cybersecurity firm Kaspersky, underscoring an uncommon partnership between state authorities and a private security company in combating organized digital crime.
The ministry said the raid led to the confiscation of servers, domain names and additional digital assets that the gang employed to orchestrate attacks and host malicious code. Although the release omitted details about the exact infrastructure, analysts acquainted with the case point out that VasyGrek has been associated with ransomware strikes and credential‑theft schemes that have affected enterprises on several continents in recent years.
Kaspersky’s participation—a Russian‑headquartered security vendor famed for its threat‑intelligence solutions—indicates that investigators used sophisticated malware‑analysis and attribution utilities to chart the group’s online presence. This type of collaboration is significant as it narrows the divide between private‑sector know‑how and public‑sector enforcement, a framework championed by cybersecurity specialists aiming for stronger countermeasures against transnational cyber threats.
Officials disclosed that three persons suspected of involvement in VasyGrek have been taken into custody, but they withheld names, ages or exact charges. The Interior Ministry stressed that these detentions form part of a wider campaign to dismantle organized cybercrime rings operating inside Russia, a priority that has sharpened under mounting international pressure to stem the export of ransomware utilities.
Analysts note that tearing down VasyGrek’s infrastructure may temporarily curb the group’s capacity to mount fresh attacks, yet the durability of cyber‑criminal ecosystems typically enables swift re‑assembly under different monikers. The episode highlights the persistent difficulty for law‑enforcement bodies to match the rapid pace at which threat actors can set up, shift, and profit from digital operations. Going forward, authorities are expected to keep surveilling the detained individuals, pursue possible prosecutions, and maintain cooperation with cybersecurity firms to forestall comparable dangers.
Comments (0)
Be the first to comment.
Join the discussion