Hackers Expose Data of More Than 3,600 Trump Mobile Users, Say Company Lacks Response Team
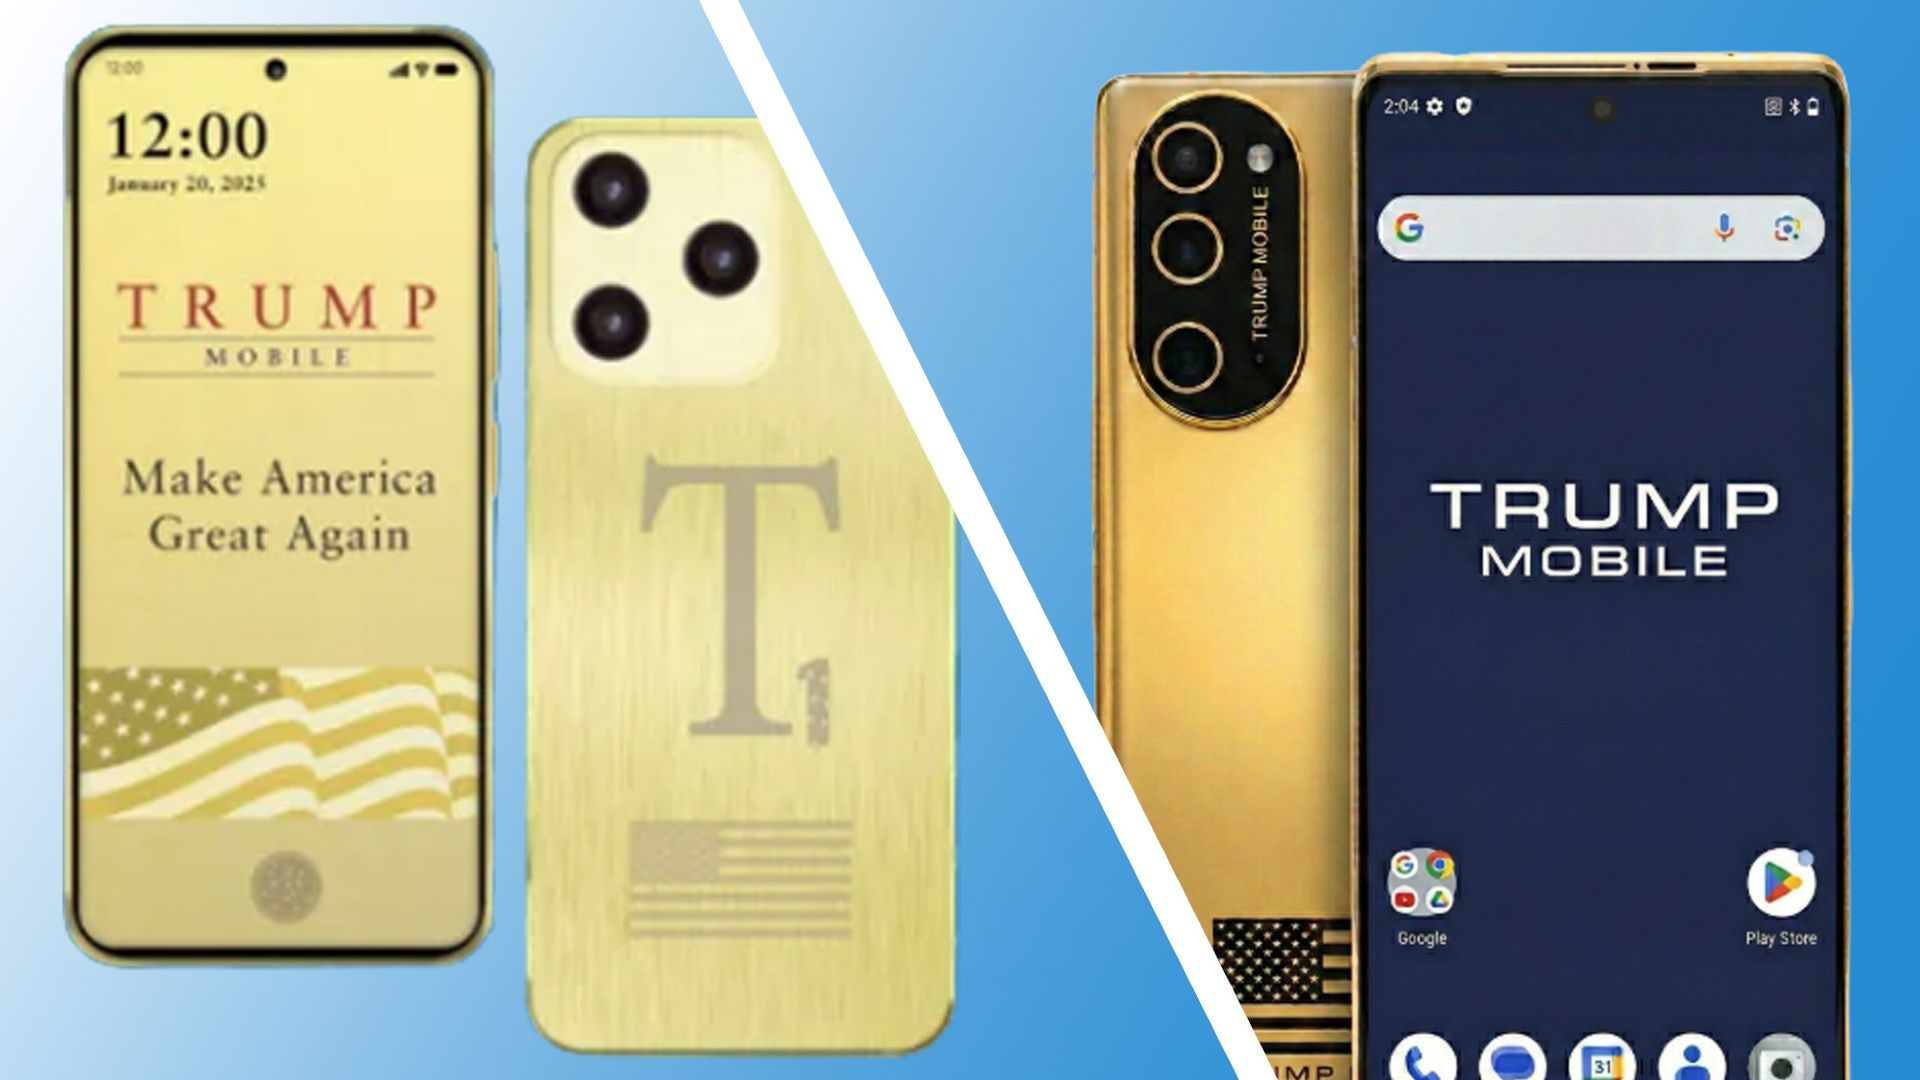
On Wednesday, the hacker group known as BYOD claimed to have published the personal information of 3,615 Trump Mobile users, the low‑cost phone line created by former President Donald Trump.
The group said the data were harvested after they installed malware on a device used by a Liberty Mobile employee—the carrier that powers the Trump brand. The exposed records list subscriber names, home addresses, phone numbers and the specifications of the phones they ordered.
Trump Mobile has offered only minimal comment. In a short response to BYOD, the firm allegedly admitted it lacks a dedicated incident‑response team, implying an absence of formal remediation resources. Liberty Mobile has not verified the breach, yet the reported attack vector highlights a typical supply‑chain flaw where threat actors infiltrate staff devices to access customer databases.
The leak exposes thousands of individuals to potential identity theft, phishing schemes and targeted scams, especially because exact home addresses are included. For customers who selected Trump Mobile as a budget-friendly substitute for premium smartphones, the incident erodes trust in the brand’s security and could hasten a shift toward carriers that provide stronger privacy protections.
Security experts observe that this breach aligns with a wider trend of attackers targeting smaller carriers and niche brands that lack the resources of larger operators. They advise impacted users to keep an eye on their credit reports, activate two‑factor authentication when available, and contemplate resetting passwords tied to the compromised services. Law‑enforcement officials have been alerted, and investigators are expected to probe whether further data from Liberty Mobile’s network was accessed.

Comments (0)
Be the first to comment.
Join the discussion